Facing Your Data Protection Fears with a GDPR Audit
Facing Your Data Protection Fears with a GDPR Audit
It’s that time of year again. The pumpkins are carved, the cobwebs are up, and everyone is bracing themselves for a few things that go bump in the night. And for data protection teams, there’s no better time for a GDPR audit.
But for many organisations, the scariest things aren’t ghosts or ghouls. They’re the data protection risks lurking quietly in the background, the forgotten spreadsheets, the unchecked suppliers, and the policies nobody has looked at since 2018. Out of sight, they can feel harmless. Until a data breach, a complaint, or a difficult Subject Access Request drags them into the light.
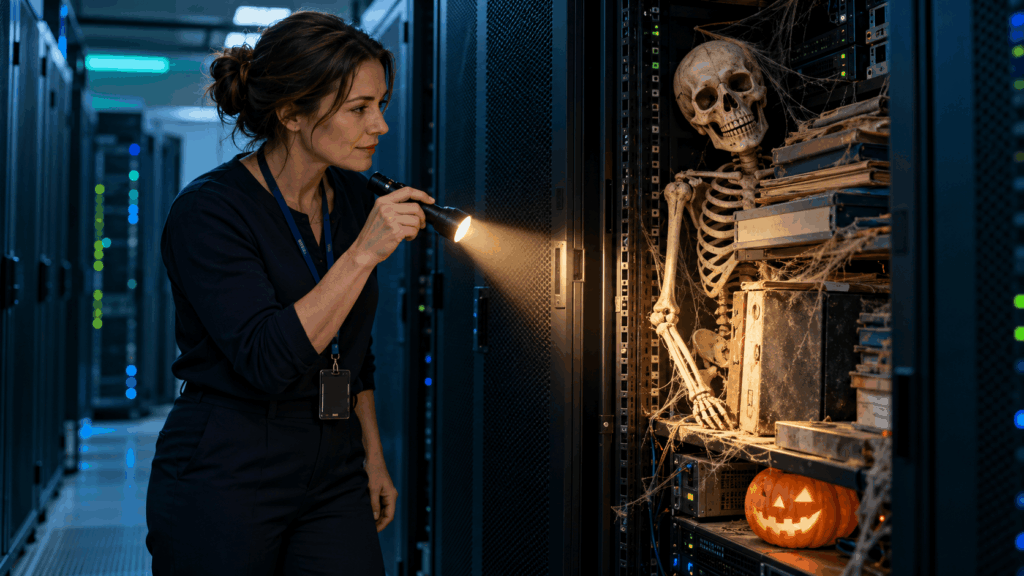
The good news? You don’t have to wait for a fright. An independent GDPR audit is the torch that lets you look into every dark corner, understand exactly what’s there, and deal with it calmly and confidently.
Six horrors hiding in your data
Every organisation is different, but our consultants see the same monsters turn up time and again.
- Zombie data Personal data that should have been deleted years ago, but keeps shuffling on. Old CVs, former customer records, and duplicate spreadsheets that no retention schedule has ever considered. Holding on to data longer than you need increases your risk and undermines the principles of data minimisation and storage limitation.
- Ghost suppliers Third parties processing personal data on your behalf with no Data Processing Agreement, no due diligence, and no clear view of where the data goes. Remember, your compliance is only as strong as your weakest link, and that includes international data transfers made without the right safeguards in place.
- Cobwebbed policies Privacy notices, the RoPA, and data protection policies, written for the original EU GDPR deadline and left untouched ever since. Legislation and ICO expectations have moved on, including recent changes under the Data (Use and Access) Act. Out-of-date documentation leaves gaps that are easy to spot and hard to defend.
- The unlocked crypt Weak access controls, shared logins, and staff who can see far more than their role requires. Your technical and organisational security measures are what stand between your personal data and a data breach.
- The thing in the attic: AI Teams experimenting with AI tools, often with the best intentions, but without a DPIA, supplier due diligence, or a governance framework. AI brings real opportunities, but it also introduces new risks that need to be identified and managed.
- The phantom SAR process A new AI driven subject access request arrives and nobody is quite sure who owns it, where the data lives or when the deadline falls. Without a clear process, individual rights requests quickly become time-consuming, stressful and risky.
Turning on the lights: how a DPAS GDPR audit works
Our GDPR audit services assess your organisation against UK & EU GDPR, the Data Protection Act 2018 and PECR, alongside recognised security standards such as ISO27001 and best practice in emerging technologies, including AI. There are no jump scares, just a clear, structured process.
- Initial discovery. We introduce your lead consultant, agree timelines and request initial documents. It’s your chance to tell us what keeps you up at night, so we can focus on the areas that matter most.
- Documentation review. We analyse your policies, procedures, and accountability documentation to see what’s really behind every closed door.
- Staff interviews and cultural understanding. Onsite or virtually, we speak with key stakeholders to understand day-to-day practices, awareness, and culture. This gives us a holistic view of how your policies and processes work in practice, not just on paper.
- Scoring and benchmarking. We assess you against our bespoke GDPR audit criteria and scoring framework, producing an overall compliance score and sectional breakdowns. Where possible, we also show how you compare with similar organisations.
- Report and action plan. You receive a detailed GDPR audit report, including an executive summary for the board, heat maps, and visual results, prioritised risks and recommendations, and a risk-based roadmap to support transformation.
- Remediation and support. We don’t leave you alone in the dark. Our consultants work with you to design and implement a remediation plan, so you can make changes confidently.
No tricks, just treats
Whether your organisation is already performing well or needs support to meet its legal obligations, an external data protection audit gives you an honest, evidence-based view of where you stand. It helps you:
- Identify vulnerabilities before they turn into a data breach or a complaint to the ICO
- Mitigate risk with pragmatic, prioritised recommendations rather than a list of problems
- Provide assurance to the board with a clear executive summary and compliance score
- Build trust with employees, customers, and new prospects, and support the sales process if you work business to business
- Raise awareness internally, promoting best practice and cultural improvements that go beyond compliance alone
Our consultants all hold, as a minimum, the BCS Practitioner Certificate in Data Protection, alongside qualifications in cyber security and a CPD practitioner level certificate in AI Governance. So you know the people holding the torch know exactly what they’re looking for.
Don’t wait for a fright
The scariest compliance gaps are the ones you don’t know about. This Halloween, swap the sense of dread for a clear, actionable roadmap and the confidence that comes with knowing exactly where you stand.
We offer a range of audits, from a full GDPR and information security audit to a condensed gap analysis, so we can support you in a way that suits your organisation and your budget.
ready to shine a light on your data protection compliance
Under UK GDPR, it isn’t enough to be compliant. You have to be able to prove it. That’s the accountability principle, and it’s exactly what the ICO will look for if a breach, complaint or difficult SAR ever puts your organisation in the spotlight.
Here’s how to get started:
- See how our GDPR audit services work, from a full GDPR and information security audit to a condensed gap analysis.
- Book a meeting with one of our consultants and tell us what’s keeping you up at night.
- Call our team on 0203 3013384.
Don’t let the skeletons stay in the server room. Book your GDPR audit consultation today and head into the new year with confidence.